
Management
AI Policy for Development Teams: Practical Rules That Work
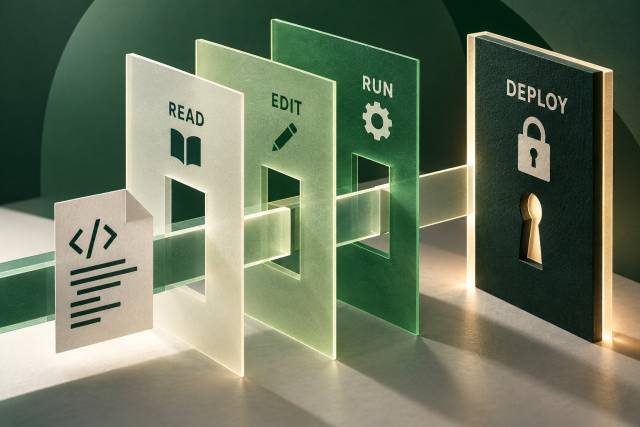
An assistant may be allowed to explain code without being allowed to run it. An AI policy for development teams needs to make that distinction usable during an ordinary task, with clear answers for data, execution, review, and ownership.
Quick answer: Publish a short operating agreement covering tools, data boundaries, review, execution permissions, and escalation. Use concrete examples, assign an owner, and update the policy when the workflow changes. Make the rules easy to find where developers work.
Write rules around ordinary scenarios
Consider these hypothetical examples:
- A developer asks an approved assistant to explain a public library API. They still verify the relevant behavior before relying on it.
- A developer wants to paste a production log. They check the data rules and remove sensitive content through the approved process before using the tool.
- An agent proposes a migration. The author reviews the change, runs the required checks, and follows the existing release approval process.
- A developer wants to connect a new external tool to a private repository. The designated owner evaluates access and data handling before connection.
The exact permitted actions depend on your organization and contracts. Use these examples to phrase rules that match those requirements and the actual development workflow.
Make an AI policy for development teams operational
DORA's guidance on a clear and communicated AI stance describes how ambiguity can lead to either excessive caution or unvetted use. The practical response is to make expectations understandable and supported.
Start with the actual tools and workflows your team uses. An approved chat assistant, a repository-connected coding agent, and an agent with shell or deployment access do not have the same capabilities.
Separate permission to suggest code from permission to execute commands, send information externally, or change a production system. Approval of one capability should not silently imply approval of all the others.
Bound agent permissions deliberately
For an agent that can act, document the environment and the permitted scope. A disposable development environment is different from a terminal authenticated to production.
Define approval boundaries for consequential actions such as deployment, destructive database changes, external communications, and access changes. Keep credentials and permissions aligned with the assigned task.
Do not assume that a natural-language instruction alone is an access-control mechanism. Where practical, enforce the boundary through the environment and tool permissions as well as the written agreement.
Define a small set of decisions
| Area | What the agreement should answer |
|---|---|
| Tools | Which products, accounts, and integrations are approved? |
| Information | What data can enter each tool, and what must be removed? |
| Output | Who checks correctness and owns submitted changes? |
| Execution | Which actions can run automatically and which need approval? |
| Uncertainty | Who answers questions and approves exceptions? |
| Incidents | How does someone report an unintended action or disclosure? |
Assign an owner for each boundary rather than making every exception a group debate. The team needs a usable path when the document does not cover a new situation.
Keep accountability with the team
The person submitting a change must understand its intended behavior and provide the required evidence. A tool's confident explanation does not transfer responsibility for acceptance.
State that AI-generated work follows the same applicable testing, review, security, and release standards as other work. Add specific controls when a tool introduces a new capability or data flow rather than creating duplicate paperwork for every use.
My guide to reviewing AI-generated PHP code shows what meaningful technical verification looks like. The policy should point to those working standards instead of repeating them inconsistently.
Provide an exception path and incident response
A useful exception request explains the task, why the approved workflow is insufficient, the proposed tool or access, and the intended duration. Record the decision so a temporary exception does not become an undocumented precedent.
For an unintended action, tell people where to report it promptly and what information to preserve. The first response should contain the problem and establish facts. A culture that punishes early reporting makes the policy harder to operate.
Keep sensitive details in the appropriate channel. A general team update can describe the process improvement without exposing private information.
Check understanding and maintain the agreement
During onboarding or a workflow change, ask developers how they would handle a few ordinary scenarios. Conflicting answers reveal unclear wording or inconsistent expectations.
Keep the current policy linked from the repository instructions or developer handbook. Record its owner and review triggers, such as a new integration, changed permissions, or an incident.
Link project-specific instructions from the repository, and connect them to the broader practical AI development workflow. Organizational policy still needs clear ownership outside a single repository.
Policy questions
Does every team need a long AI policy?
No. A small team can begin with a concise operating agreement that covers its real tools, data, verification, and permissions. The document should grow only when additional complexity requires it.
Is an approved tool safe for every kind of data?
Do not assume so. Approval should specify the account, configuration, and permitted information. Different integrations and settings can create different data flows.
Who owns code written by an AI assistant inside the workflow?
For engineering accountability, the submitting author and the team's acceptance process remain responsible for verifying the change. Questions about legal ownership or licensing require the appropriate organizational review.
If your team needs practical AI workflow boundaries, my AI development consulting can help connect the operating agreement with the repository and delivery process.