
Development
Where Should Human Approval Sit in an AI Workflow?
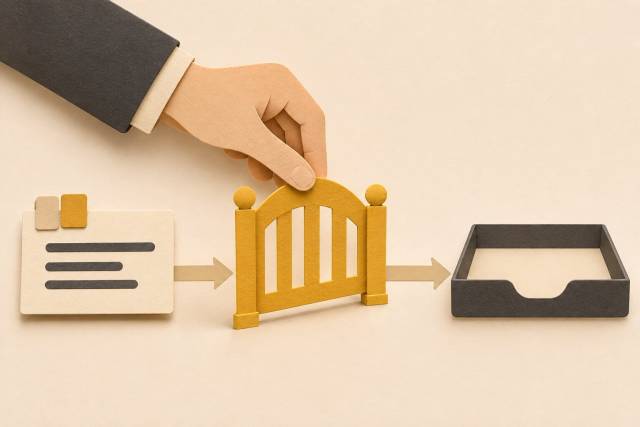
Place human approval in an AI workflow after the proposed action is concrete enough to inspect and before the system carries it out. The reviewer should see the actual target, intended change, supporting evidence and consequences. The execution component should then verify that the approved proposal is still the action it is about to perform.
That does not mean interrupting a user after every model response. Decide which actions require a fresh decision and which may run within an explicitly authorized, bounded policy. The boundary should follow the action and its authority, not whether the model sounds confident.
Put human approval at the AI workflow's action boundary
Mapping the workflow helps identify the useful checkpoint. Separate gathering permitted information, preparing a proposal, reviewing it, and carrying out the approved operation.
Drafting a message is different from sending it. Suggesting a configuration change is different from applying it. Summarizing permitted information can still be consequential if the summary is sent to someone who may not see the underlying data.
For each action, ask who or what it affects, whether it crosses a permission boundary, and what recovery would require. Reading sensitive material needs authorization before access, even when it creates no external write. A final approval screen cannot undo an earlier disclosure.
Anthropic's Building effective agents distinguishes predefined workflows from systems where a model directs its own steps, and discusses human checkpoints. That is a useful conceptual distinction, not a guarantee that any particular framework enforces your policy. The article itself notes that its tooling landscape has evolved.
Give the reviewer an action they can actually assess
“Approve the AI's plan” is too vague if the recipient, data, or scope will be chosen later. Prepare the concrete operation first, without performing it.
A reviewable proposal should identify:
- The operation, target account or environment, and affected resource
- The exact proposed content or change, including the recipient for communications
- The evidence supporting the choice and any unresolved uncertainty
- The expected effect and available recovery path
- The revision being reviewed and the limits of the requested authority
Show the meaningful change directly. A summary can help the reviewer navigate, but it should not hide the actual message, target, or changed setting behind an unsupported assurance that everything looks safe.
OWASP's human-in-the-loop guidance recommends evaluating consequential tool actions before execution and verifying approval for the specific operation. A prompt that tells the model to ask first is not, by itself, an execution gate.
Keep enforcement outside the model
Treat the model's output as a proposed action. Let application code decide whether the authenticated caller may request it, whether the designated reviewer may approve it, and whether the approval covers the operation presented to the execution tool.
For a proposed design, keep an action record with a stable identifier and a revision representing the reviewed fields. Store the approval decision against that record. The model can explain the proposal, but it should not be able to invent a reviewer identity or mark its own action approved.
The tool boundary should reject requests that omit approval when policy requires it. Apply the same rule to alternate routes, background jobs and resumed workflows. A well-designed review page is ineffective if another execution path ignores its decision.
Approval also does not expand the tool's permissions. A reviewer should not be able to authorize access they do not hold, and a broadly privileged service account should not silently turn a narrow approval into wider authority.
Invalidate approval when the proposal or context changes
Approval belongs to the reviewed operation. If a message changes recipient, an action changes environment, or the proposed modification changes, return it for review rather than carrying the old decision forward.
Check the relevant state again immediately before the side effect. If the resource revision or permission state no longer matches the assumptions under review, stop and reconcile. Where concurrent changes are possible, use an execution mechanism that can enforce the expected revision rather than leaving a gap between checking it and writing.
Define how long pending approvals remain usable, when they can be revoked, and what happens when the reviewer loses authority. The appropriate lifetime depends on the action and how quickly its context changes. A universal timeout is less useful than a clear rule tied to that risk.
Keep the outcome distinct from the approval. “Approved” means someone authorized a particular operation. It does not prove the operation ran, reached its destination, or produced the desired result.
Walk through a hypothetical approval flow
Consider an AI feature that prepares an invoice email for a staff member to review. This is an illustrative design, not a report of a customer implementation or a tested software package.
| State | What the system should establish |
|---|---|
| Proposed | A draft recipient, message and attachment selection exist without sending. |
| Awaiting review | The reviewer can inspect those exact fields and the supporting record. |
| Approved | An authorized reviewer has accepted that specific proposal revision. |
| Executing | The application has rechecked approval, permissions and relevant record versions. |
| Completed | The execution service has supplied evidence of the operation's result. |
| Rejected, expired or changed | Execution stays unavailable until the applicable decision is resolved. |
Suppose the recipient changes after review. That creates a different proposal requiring a new decision. Suppose sending times out with an uncertain result. Do not interpret the missing response as proof that nothing happened and send again blindly. Reconcile the operation's recorded identity and provider result before choosing a retry or recovery action.
The useful audit trail connects proposal, revision, reviewer, execution attempt and observed outcome. Record enough to explain the decision while respecting the system's data-retention and access rules. Do not turn the review log into an unnecessary copy of every sensitive attachment.
Test the boundary before widening autonomy
Use disposable data and sandboxed execution substitutes. Demonstrate that the system handles more than the successful approval path:
- A user rejects the proposal or leaves it unanswered.
- Someone tries to execute without a required approval.
- A recipient, target, resource revision or material action field changes after approval.
- The reviewer's authority is revoked before execution.
- The same approved operation is submitted twice.
- Execution fails or returns an ambiguous result.
For each scenario, define the expected application behavior and observe tool calls and state changes. A reassuring final model response is not evidence that an unauthorized operation was prevented. These checks establish evidence for the scenarios you tested, not a guarantee against every failure.
Review workload matters too. Repeatedly presenting low-value confirmations can make meaningful decisions harder to notice. Start with a narrow workflow, keep routine work within its agreed authority, and reserve fresh review for actions that need it. Measure queue age, unresolved decisions and correction work before increasing the scope of unattended actions.
Decide whether you need a review or implementation help
A focused workflow review fits when the team cannot explain which actions require approval, what a reviewer sees, or which execution paths enforce the decision. Ask for an action inventory, an authority map, proposed checkpoints, and a test plan tied to observable outcomes.
Hands-on implementation fits when those decisions are agreed but the product needs the pending-action state, review interface, execution checks, or recovery behavior built and verified. Agree on one bounded workflow and its acceptance cases before expanding it to every tool.
The knowledge-base preparation guide addresses the information the AI consumes. The AI operating-cost guide helps account for review effort and retries. Approval placement is a separate design decision about when a proposed operation may become an actual effect.
Does every AI step need human approval?
No. Follow the application's permission model and the user's agreed scope. Some routine actions may already be authorized under a bounded policy. Require a new decision where the proposed action exceeds that scope or the policy calls for one, and keep the boundary enforceable in the application.
Is an approval button enough?
No. The execution path must check the right person's approval for the actual operation, reject changed or stale proposals, and report what happened afterward. Human review helps make a decision; it does not replace access control, validation, or testing.
If your team is deciding where an AI feature should pause before acting, discuss a focused AI workflow review around the concrete actions, authority and evidence first.